Understanding roughly how account theft happens makes it much easier to spot. This is a defensive overview, written so you can recognise the patterns rather than fall for them.
Need another section? Start with the Delta Executor homepage, use the Delta Executor download hub for platform files and setup routes, read the Delta Executor key guide, or browse the Delta Executor scripts library.
There are four broad approaches and they show up constantly in the executor and scripting scene.
1. Fake Login Pages
The most common and the simplest. A page that looks like Roblox asks you to log in, and it sends what you type somewhere else.
These appear inside modified executor builds, on key system pages, on reward sites and in Discord servers. The copies are often visually perfect.
Defence: never enter Roblox credentials anywhere except roblox.com or the official app. Appearance proves nothing.
2. Session Token Theft
Roblox keeps you logged in using a token stored on your device. Anything with sufficient access to your browser or device can potentially read it.
This is significant because a stolen token bypasses two step verification entirely. The thief does not need your password.
This is why requests for your .ROBLOSECURITY value are always malicious, and why pasting it anywhere for any reason is a mistake.
Defence: never share it, and be cautious about what you install and what browser extensions you allow.
3. Malicious Scripts
A script is code, and code can do more than it claims. A script advertised as auto farm can also send information elsewhere.
Obfuscated scripts, meaning code deliberately made unreadable, are common here. There are occasionally legitimate reasons for obfuscation, but it also conveniently hides behaviour from anyone checking.
Defence: prefer scripts from sources with a track record, be wary of unreadable code from unknown sources, and be suspicious of a script that requests anything account related.
4. Repackaged Apps
A modified version of a legitimate app, rebuilt with extra functionality and redistributed under the real name.
These work exactly as expected while doing something additional. The usual mechanism is broad permissions, particularly accessibility services, which can observe what is displayed and typed.
Defence: check file size, file type and permissions after install. This is the check that catches repackaged builds.
Warning Signs Across All Four
| Sign | What it suggests |
|---|---|
| Any request for Roblox credentials | Phishing |
| Request for your .ROBLOSECURITY cookie | Token theft |
| Accessibility or device admin permission | Repackaged app |
| Obfuscated script from an unknown source | Possible malicious script |
| Unexpected browser pages opening | Something installed alongside |
| Friends receiving messages you did not send | Account already compromised |
Signs Your Account Is Already Compromised
- Trades or purchases you did not make.
- Friend requests sent from your account.
- Items missing from your inventory.
- Password reset emails you did not request.
- Being logged out unexpectedly.
- Messages sent to your friends that you did not write.
If you see any of these, act immediately using the steps below.
Response Steps
- Change your Roblox password from a different device.
- Enable two step verification.
- Log out all sessions in Roblox security settings.
- Change your email password, from a different device.
- Review trades and purchases, and report anything unauthorised to Roblox.
- Remove any recently installed app or extension you do not fully trust.
- Warn friends who may have received messages from your account.
The Core Defences
Three things prevent most of this.
Two step verification, which makes a stolen password insufficient on its own.
Never sharing credentials or session tokens, which closes the two most direct routes.
Checking permissions after installing anything, which catches repackaged apps before they do damage.
Frequently Asked Questions
Can someone steal my account just from me visiting a website? Visiting a page alone is very unlikely to be enough. Entering credentials or installing something from it is where the risk lies.
Does two step verification make me safe? It removes the most common attack. It does not protect against session token theft, which is why token sharing must be refused as well.
Can Roblox recover a stolen account? Often yes through account recovery, particularly if you act quickly and can verify ownership.
How do I know if a script is malicious? You cannot always tell, which is why source matters. Unreadable code from an unknown source is a reasonable thing to refuse.
Related reading
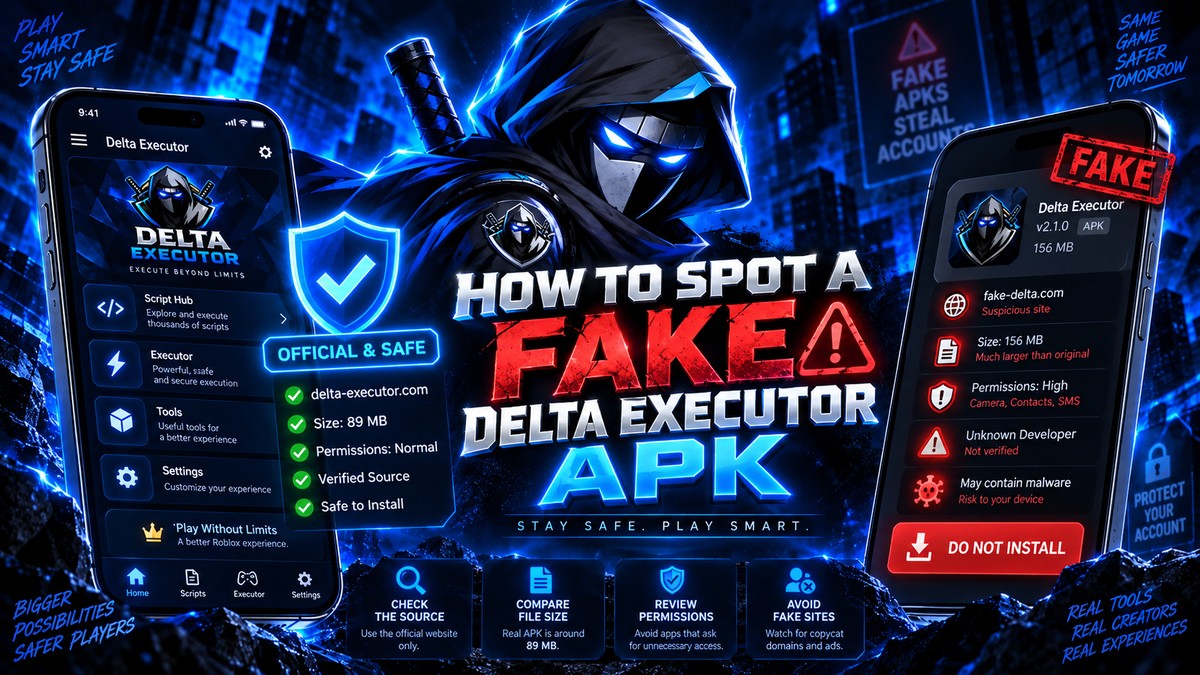
How To Spot A Fake Delta Executor APK
Five checks that tell you whether a Delta Executor download is genuine or repackaged, including file size, permissions and installer behaviour.
Read more
Delta Executor Permissions Explained In Full
Every permission Delta Executor should and should not request on Android, and which ones mean the file has been tampered with.
Read more
Why Antivirus Flags Delta Executor
Why security software marks Delta Executor as a threat, how to tell a false positive from a real one, and safer options than disabling protection.
Read more